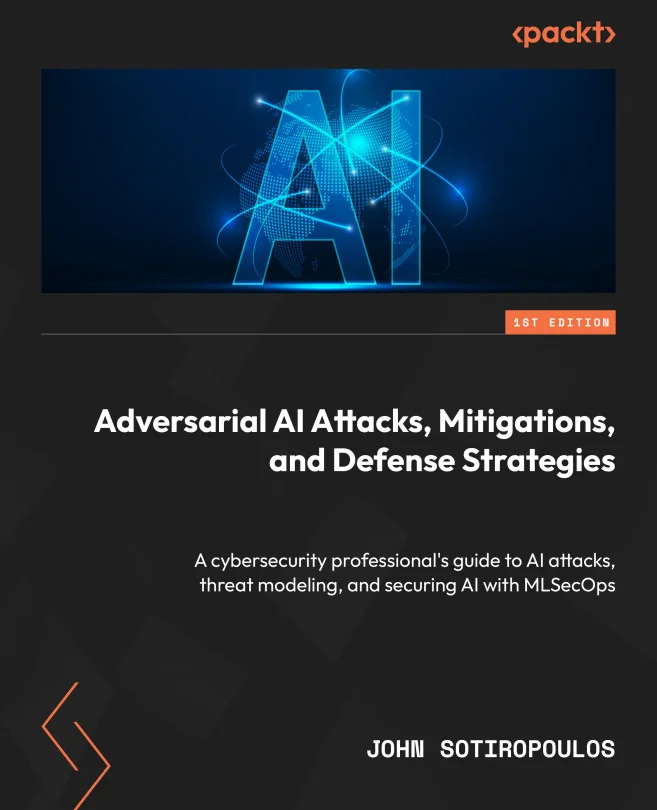
Adversarial AI Attacks, Mitigations, and Defense Strategies
A cybersecurity professional's guide to AI attacks, threat modeling, and securing AI with MLSecOps
Created by John Sotiropoulos
Explore the world of adversarial AI attacks and learn how to protect your systems from manipulation, evasion, and privacy threats. Gain practical skills to defend AI models against poisoning, theft, and tampering, ensuring your AI remains secure and trustworthy.
Packt | Jul 2024 | 602 min
What You Will Learn
You will build hands-on experience by working through real-world scenarios and practical examples that show how adversarial attacks are performed and mitigated. Step-by-step guidance will help you set up test environments, analyze threats, and implement defense strategies using proven frameworks and tools.
Key Features
- Identify and counter adversarial attacks like poisoning, model theft, and prompt injection
- Apply threat modeling and secure-by-design principles to safeguard AI systems
- Integrate MLSecOps and DevSecOps practices for robust AI security management
Target Audience
Designed for AI developers, engineers, and cybersecurity professionals with a basic understanding of security, machine learning, and Python. If you want to strengthen your skills in defending AI systems or are responsible for securing enterprise AI, you'll find actionable strategies and practical insights to meet your goals.
Related courses